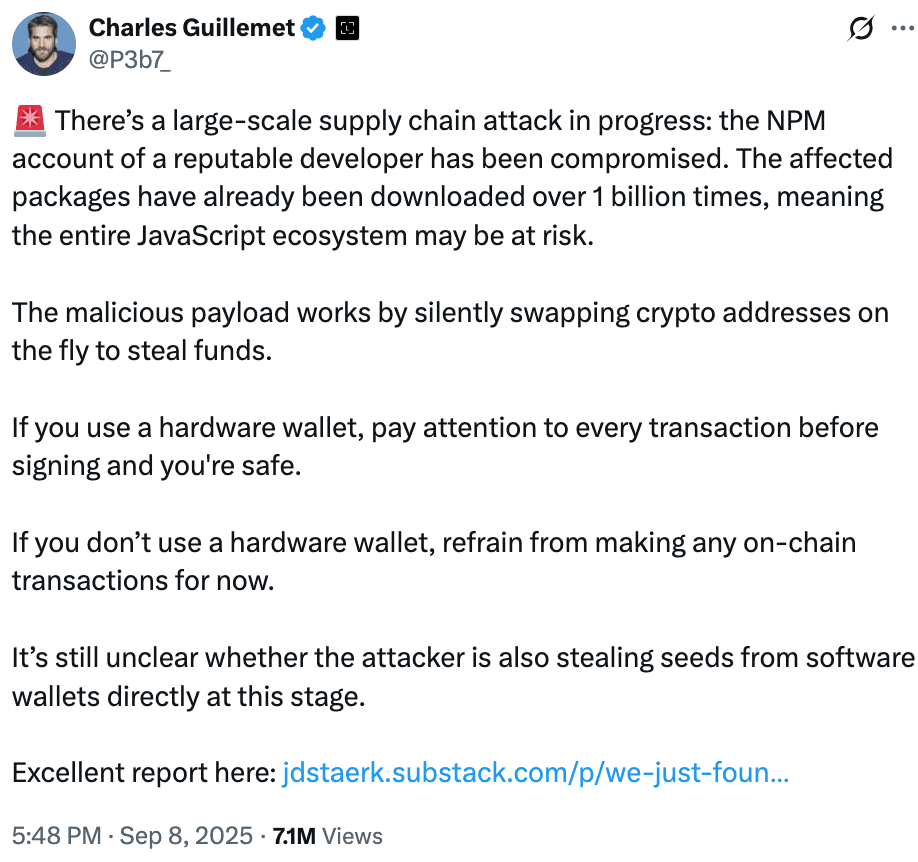
8 सितंबर को, एक बड़े सॉफ्टवेयर supply chain attack ने NPM ecosystem को हिट किया, जिससे कई व्यापक रूप से इस्तेमाल की जाने वाली JavaScript libraries compromise हो गईं। यह breach तब सामने आया जब Ledger के Chief Technology Officer, Charles Guillemet ने चेतावनी दी कि एक भरोसेमंद developer का Node Package Manager account hijack कर लिया गया है। शुरुआती अनुमानों में exposure 1 billion downloads से अधिक बताया गया था, लेकिन आगे के analysis से पता चला कि compromised packages वास्तव में 2.6 billion से अधिक weekly downloads का प्रतिनिधित्व करते हैं।

Supply Chain Attack Exposes Over 2 Billion
Supply Chain Attack Exposes Over 2 Billion
"qix" नाम के एक developer के account को target किया गया, जो chalk, strip-ansi, color-convert, और debug जैसी कई popular JavaScript libraries को maintain करते हैं। ये libraries server-side और front-end environments दोनों में अनगिनत projects में दिखाई देती हैं। attackers ने एक fake support email के जरिए access हासिल किया और लगभग 18 packages में malicious updates push कर दिए। automated dependency installs ने malware को कुछ ही घंटों में तेजी से फैलने की अनुमति दी।
Guillemet ने बताया कि malicious code ने transactions के दौरान चुपचाप cryptocurrency wallet addresses को replace कर दिया। जो users software wallets पर भरोसा करते हैं, उन्हें funds खोने का जोखिम था यदि उन्होंने बदले हुए recipient address पर ध्यान दिए बिना transactions approve कर दिए।
Malware Crypto Clipper and MetaMask
Security researchers ने इस malware को "crypto clipper" के रूप में classify किया है। यह transaction के विभिन्न stages पर wallet addresses को replace कर देता है। जब कोई wallet detect नहीं होता है, तो malware browser functions जैसे fetch और XMLHttpRequest में hook करके decentralized applications के भीतर outgoing data को modify कर देता है, जिससे application data के भीतर addresses scan और alter हो जाते हैं।
यदि MetaMask जैसा कोई wallet extension मौजूद है, तो malware signing से पहले transaction को intercept कर लेता है। यह memory में wallet address को modify कर देता है ताकि जब user transaction review करे, तो fraudulent address दिखाई दे। malware Levenshtein algorithm का उपयोग करके ऐसे addresses generate करता है जो original से काफी मिलते-जुलते हैं, जिससे बदलावों को पहचानना मुश्किल हो जाता है।
Supply Chain Attack Exposes Over 2 Billion
First Signs of the Attack
Developers ने पहली बार attack को तब नोटिस किया जब build systems ने एक unexpected error message return किया। error-ex नामक dependency के inspection से obfuscated code का पता चला जिसमें checkethereumw नामक एक संदिग्ध function था, जो Ethereum wallet को target करने का संकेत देता है। analysts ने पुष्टि की कि malware में कई blockchains पर wallet addresses के references शामिल थे, जिनमें Bitcoin, Ethereum, Solana, Tron, Litecoin, और Bitcoin Cash शामिल हैं।
प्रभावित packages में JavaScript ecosystem में सबसे अधिक उपयोग किए जाने वाले कुछ packages शामिल हैं। Chalk को 300 million से अधिक weekly downloads, debug को 350 million से अधिक, और strip-ansi को 260 million से अधिक downloads मिलते हैं। कुल मिलाकर, compromised libraries को हर हफ्ते 2.6 billion से अधिक बार download किया जाता है, जो developer community पर प्रभाव के पैमाने को दर्शाता है।
Hardware vs Software Wallets
कई infected libraries सीधे cryptocurrency projects से जुड़ी नहीं हैं, लेकिन dependency chains में उनके integration का मतलब है कि unrelated applications भी expose हो सकती हैं। जो projects cryptocurrency wallets और decentralized applications के साथ interact करते हैं, उन्हें सबसे अधिक जोखिम का सामना करना पड़ता है।
Guillemet ने नोट किया कि clear-signing features वाले hardware wallets के users सुरक्षित हैं क्योंकि ये devices approval से पहले हर transaction के verification की अनुमति देते हैं। software wallet users को अधिक exposure का सामना करना पड़ता है और उन्हें तब तक अत्यधिक सावधानी बरतनी चाहिए जब तक कि dependencies की पूरी तरह से review और security सुनिश्चित न हो जाए।
Finding the Attacker and Funds Stolen
attacker के cryptocurrency addresses की पहचान कर ली गई है और public blockchain transparency के माध्यम से उनकी सक्रिय रूप से निगरानी की जा रही है। operation से जुड़ा एक primary Ethereum address 0xFc4a4858bafef54D1b1d7697bfb5c52F4c166976 है, साथ ही कई backup addresses भी हैं। reporting के समय तक, चोरी किए गए funds को move नहीं किया गया था। यह monitoring ongoing analysis को सक्षम बनाती है, हालांकि चोरी की गई assets का पूरा दायरा अभी भी स्पष्ट नहीं है।
Supply Chain Attack Exposes Over 2 Billion
JavaScript and Community Role
JavaScript और web3 communities ने incident को contain करने के लिए तेजी से कदम उठाए। compromised packages के malicious versions को registry से काफी हद तक हटा दिया गया है, लेकिन उन projects के लिए जोखिम बना हुआ है जो अभी भी अपने lockfiles में पुराने versions पर निर्भर हो सकते हैं। developers से आग्रह किया जा रहा है कि वे अपनी dependencies का audit करें, safe versions को lock करें, और आगे के exposure को रोकने के लिए clean builds को reinstall करें।
security professionals सलाह देते हैं कि developers credentials rotate करें, NPM और GitHub जैसे accounts पर two-factor authentication लागू करें, और strict version control बनाए रखने के लिए npm ci जैसे deterministic installation methods का उपयोग करें। users को सभी cryptocurrency transactions को सावधानीपूर्वक verify करना चाहिए, विशेष रूप से जब software wallets पर भरोसा कर रहे हों।
Final Thoughts
यह incident NPM ecosystem को हिट करने वाले सबसे व्यापक breaches में से एक है। हालांकि community का response अपेक्षाकृत तेज था, लेकिन यह attack modern software supply chains की fragility और open-source components पर व्यापक निर्भरता से पैदा होने वाले जोखिमों को उजागर करता है।
जैसा कि Guillemet ने जोर दिया, signing से पहले हर transaction की review करना आवश्यक है। यह breach दर्शाता है कि application infrastructure में गहराई से embedded छोटी libraries भी compromise होने पर महत्वपूर्ण attack vectors बन सकती हैं। developers और users दोनों के लिए, web3 और software development ecosystems में security बनाए रखने के लिए निरंतर सतर्कता अब एक महत्वपूर्ण हिस्सा है।